Digital Task Force - ISMS supports organizations in protecting cardholder data and meeting PCI-DSS requirements.
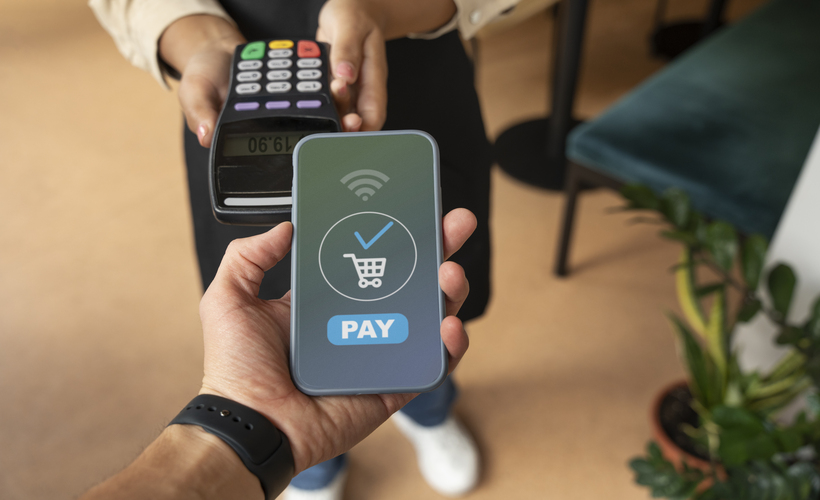
Identification and Assessment of Systems, Networks, and Processes that store, process, or transmit cardholder data.
Evaluation of Segmentation Controls, Firewall Rules, and access mechanisms to limit CDE exposure and reduce compliance scope.
Review of Logging, Monitoring, Encryption, and key management controls protecting cardholder data.
Detailed assessment of existing controls against PCI-DSS requirements to Identify Gaps and Non-Compliances.
Practical guidance on implementing technical and procedural controls to close identified gaps.
Support in coordinating with Approved Scanning Vendors (ASVs) for External Vulnerability Scans and Compliance Validation.
Clear, structured report outlining Compliance Status, Gaps, and alignment with PCI-DSS requirements.
Prioritized remediation plan with Clear Actions, Ownership, and timelines to achieve Compliance.
PCI-DSS is a Global Security standard designed to protect cardholder data in payment environments.
Any organization that Stores, Processes, or transmits cardholder data must comply with PCI-DSS requirements.
Yes. PCI-DSS is Mandatory for Payment Gateways, Fintechs, Banks, and merchants handling card data.
Digital Task Force - ISMS Provides PCI-DSS Advisory, Gap Assessment, and Remediation Support. Formal QSA Attestations are issued by licensed QSAs.
Whether you are navigating the complexities of the DPDP Act 2023, requiring an urgent CERT-In Incident Response, or strengthening your defenses with a VAPT Audit, Digital Task Force - ISMS is ready to deploy.

© 2026 Digital Task Force - ISMS
